Maintaining uninterrupted and secure access to online gaming accounts requires careful digital navigation. As primary gaming portals frequently undergo domain migrations, scheduled maintenance, or network-level DNS filtering, operators regularly deploy alternative links often called mirror domains or backup URLs to ensure player access remains smooth.
However, the widespread use of backup links has given rise to sophisticated cyber threats. Phishing networks frequently clone official landing pages to steal user login credentials, intercept financial deposits, and install tracking scripts. Distinguishing between a genuine backup URL and a dangerous malicious proxy is an essential skill for any active user.
This comprehensive guide outlines the key technical traits, security indicators, and verification steps needed to identify authentic, phishing-free alternative slot links.
Understanding the Security Risks of Fake Alternative Links
Before analyzing how to verify genuine mirror links, it is important to understand how fraudulent operators construct fake portals and what dangers they pose to users.
The Mechanics of Domain Cloning and Typosquatting
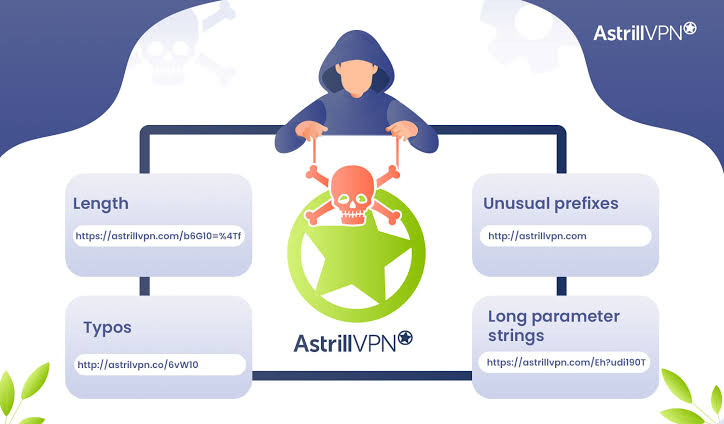
Cybercriminals rarely create online portals from scratch; instead, they scrape and duplicate the visual assets of legitimate brands. They register domain names using “typosquatting” a technique that relies on common typos, subtle letter swaps, or alternative top-level domains (TLDs) such as .xyz, .top, .info, or .work.
When a user visits a typosquatted domain, the visual layout, branding logos, and color palettes appear identical to the official platform. However, the backend is connected to a rogue server designed to capture raw text entries from input fields.
Data Harvesting and Account Hijacking
The primary objective of a phishing clone is credential harvesting. Once a user inputs their username and password into a fake login box, the data is instantly saved to an unauthorized database.
Attacking entities can use these harvested credentials to:
- Access the user’s real account on the official server and drain remaining credit balances.
- Intercept pending withdrawal requests and alter payout destination details.
- Sell aggregated user lists (emails, passwords, phone numbers) on unauthorized data forums.
- Attempt automated credential stuffing attacks across email providers, digital wallets, and banking portals.
Rogue Deposit Gateways and Financial Interception
Beyond stealing login information, advanced phishing portals embed fraudulent payment processing forms. When a user attempts to make a deposit through a cloned portal, the site displays fake QR codes, unverified virtual account numbers, or fraudulent e-wallet destinations.
Because these payment gateways are disconnected from the official platform’s accounting system, transferred funds disappear instantly into third-party accounts, with no credit applied to the player’s gaming balance.
Key Characteristics of Phishing-Free Alternative Links
Recognizing a secure alternative URL requires looking past surface-level visual design and inspecting the underlying technical architecture. Authentic mirror links display several distinct technical characteristics.
1. Robust SSL/TLS Cryptographic Protocols
The first line of defense when evaluating any alternative domain is inspecting its transport layer security.
- Strict HTTPS Prefixes: A legitimate alternative link will always use https:// protocols rather than unencrypted http://. Modern web browsers display a secure padlock icon next to authentic HTTPS URLs.
- Valid Certificate Authority (CA): Clicking the padlock icon reveals the domain’s SSL/TLS certificate. Genuine alternative links use certificates issued by recognized, trusted Certificate Authorities (such as Let’s Encrypt, Cloudflare, DigiCert, or Sectigo).
- Domain Identity Alignment: Inspecting the certificate details confirms that the issued domain hierarchy matches the official operational network of the platform operator.
2. Seamless Single Sign-On (SSO) and Database Continuity
An official alternative link is not an independent website; it is simply a different entrance to the exact same centralized server and database infrastructure.
- No Re-Registration Required: A genuine mirror link recognizes your pre-existing login credentials immediately. If an alternative URL claims that your username or password is invalid and prompts you to fill out a “New User Registration” form, exit the site immediately. This is a major indicator of a credential-harvesting attempt.
- Instant Data Synchronization: Upon logging into an authentic backup domain, your historical data including active credit balance, loyalty tiers, pending bets, deposit records, and personal account settings will be fully populated and up to date.
3. Complete Deep-Link Structural Integrity
Phishing operators usually copy only high-visibility landing pages, leaving deeper site structures incomplete or non-functional.
- Functional Footer Links: Scroll to the bottom of the page and click secondary documentation links, such as “Terms & Conditions,” “Privacy Policy,” “Responsible Gaming,” and “Provider Licenses.” Genuine mirror links maintain full navigational structure leading to complete, readable documents. Phishing sites frequently use dead text, # anchors that reload the page, or broken 404 links.
- Broad Provider Catalog Access: Authentic links maintain dynamic connections to external software provider game servers. Clicking through different game categories should launch game client preview frames correctly, rather than resulting in infinite loading screens or script error messages.
4. Interactive and Live Support Infrastructure
Customer service channels provide a clear test for site authenticity.
- Active Live Chat Systems: Genuine mirror portals embed real-time, interactive chat widgets that connect immediately to customer service representatives without requiring external file downloads.
- Verified Communication Handles: Live support agents on an authentic mirror link will confirm your account details securely and verify the current domain address against the operator’s main index. Fake portals either feature static chat graphics that do not open, or redirect users to unverified third-party messaging accounts.
Technical Inspection Protocols for Everyday Users
You do not need to be a cybersecurity specialist to run basic technical checks on a suspicious alternative URL. Performing a few simple inspections before logging in will protect your device and data.
Inspecting Domain Syntax for Subtle Alterations
Cybercriminals rely on visual tricks to fool casual observers. Before entering any credentials, carefully analyze the URL text string in your browser address bar.
- Look for Extra Hyphens and Numbers: Attackers often take a brand name like officialbrand and register domains such as official-brand-link12.com or officialbrand-login-sec.net.
- Watch for Character Substitutions: Check for visual character swaps, such as replacing the letter o with the number 0, or replacing l (lowercase L) with 1 (one) or i (capital I).
- Check the Top-Level Domain (TLD): Established platforms typically utilize standardized TLDs or maintain consistent, documented domain extensions. Be cautious when encountering unfamiliar, low-cost TLD extensions that differ from the brand’s verified domain patterns.
Verifying Network Responses and Redirection Chains
When you enter an alternative URL, observe how the browser navigates to the destination page.
- Avoid Multi-Hop Redirection Loops: If clicking a link causes your browser to flash through several intermediate web addresses before settling on a final landing page, you may be passing through an unauthorized affiliate tracking network or a traffic-monetization proxy.
- Utilize Online URL Scanners: If you suspect an alternative link might be unsafe, run the URL through free, publicly available domain analysis tools (such as VirusTotal or Securi SiteCheck) before opening it in your browser. These tools scan the target domain for known malicious scripts, blacklist status, and suspicious IP hosting locations.
Safe Retrieval Methods for Alternative Slot Links
Finding reliable, phishing-free alternative links requires using trusted communication pathways instead of relying on open search engine results.
1. Utilizing Pre-Saved Official Bookmarks
The most effective way to avoid phishing portals is securing legitimate backup links while connected to the primary site during normal operations.
- Create a Secure Bookmark Folder: While logged into the main platform, navigate to their official announcement section or footer menu where official backup domains are listed. Save these direct links inside a dedicated browser folder.
- Store Official Contact Cards: Copy verified support email addresses, official messaging accounts, and primary domain URLs into a secure personal note or document for easy access during access disruptions.
2. Contacting Authenticated Support Channels
If primary domains become unreachable and pre-saved links fail, rely exclusively on direct support pathways to request active alternative links.
- Verified Social Media Handles: Reach out to official, verified social media channels. Look for official platform verification badges, established account creation dates, consistent posting histories, and direct profile links back to the main domain.
- Direct Email Inquiries: Send a clear request to the platform’s official customer support email address. Genuine organizations respond with cryptographically authenticated domain emails containing current, verified alternative URLs.
3. Avoiding High-Risk Search Queries
Executing broad web searches using terms like “latest active slot gacor link” or “free alternative slot URL” often leads to unsafe results. Cybercriminals heavily optimize malicious blog posts and unauthorized landing pages to capture this traffic. Always bypass unverified third-party search results in favor of official channel communications.
Digital Hygiene Practices for Long-Term Account Protection
Applying advanced security habits across your devices creates a strong defense against digital threats, ensuring your session remains secure even if you encounter a suspicious link.
Utilizing Dedicated Password Managers
Never rely on memory or simple password patterns across multiple platforms. Using a reputable, encrypted password manager provides several distinct security advantages:
- Automated Phishing Prevention: Most modern password managers use domain-matching logic to auto-fill saved passwords. If you land on a cloned phishing site (e.g., officia1brand.com instead of officialbrand.com), the password manager will not recognize the domain name and will refuse to auto-fill your credentials, alerting you to the fake site.
- Unique Password Generation: Password managers allow you to create long, complex, randomized password strings for every site you use, eliminating the risk of cross-account compromise.
Enabling Multi-Factor Authentication (MFA)
Multi-Factor Authentication (MFA) or Two-Factor Authentication (2FA) provides a crucial layer of security for user accounts.
- Time-Based One-Time Passwords (TOTP): Link your gaming profile to an authenticator application (such as Google Authenticator, Microsoft Authenticator, or Authy).
- Secondary Verification Barrier: With MFA enabled, even if an unauthorized third party captures your password via a fake login form, they cannot access your account without the temporary, numeric verification code generated by your physical authentication device.
Securing Browser Environments and Keeping Systems Updated
Your local browsing environment plays a vital role in preventing malicious script execution.
- Keep Browsers Updated: Regularly update your web browser (Chrome, Firefox, Edge, Safari) to ensure you have the latest security patches, anti-phishing filters, and revoking mechanisms for compromised SSL certificates.
- Configure Built-in Protection Features: Ensure your browser’s default security settings such as Google Safe Browsing or Microsoft Defender SmartScreen are set to “Enhanced Protection” to block connection attempts to known malicious sites automatically.